Access Control
Authentication verifies identity. Authorization determines what that identity can do.
PostgreSQL GRANT and REVOKE provide precise control. Privilege problems usually arise from missing default conventions. Examples include making an application account the owner, retaining temporary superuser access after troubleshooting, and omitting grants on new tables.
Pigsty provides four role tiers, default privileges, and database isolation. This starting model reduces manual grants per database. Operators must still assign roles to match business boundaries and regularly review effective privileges.
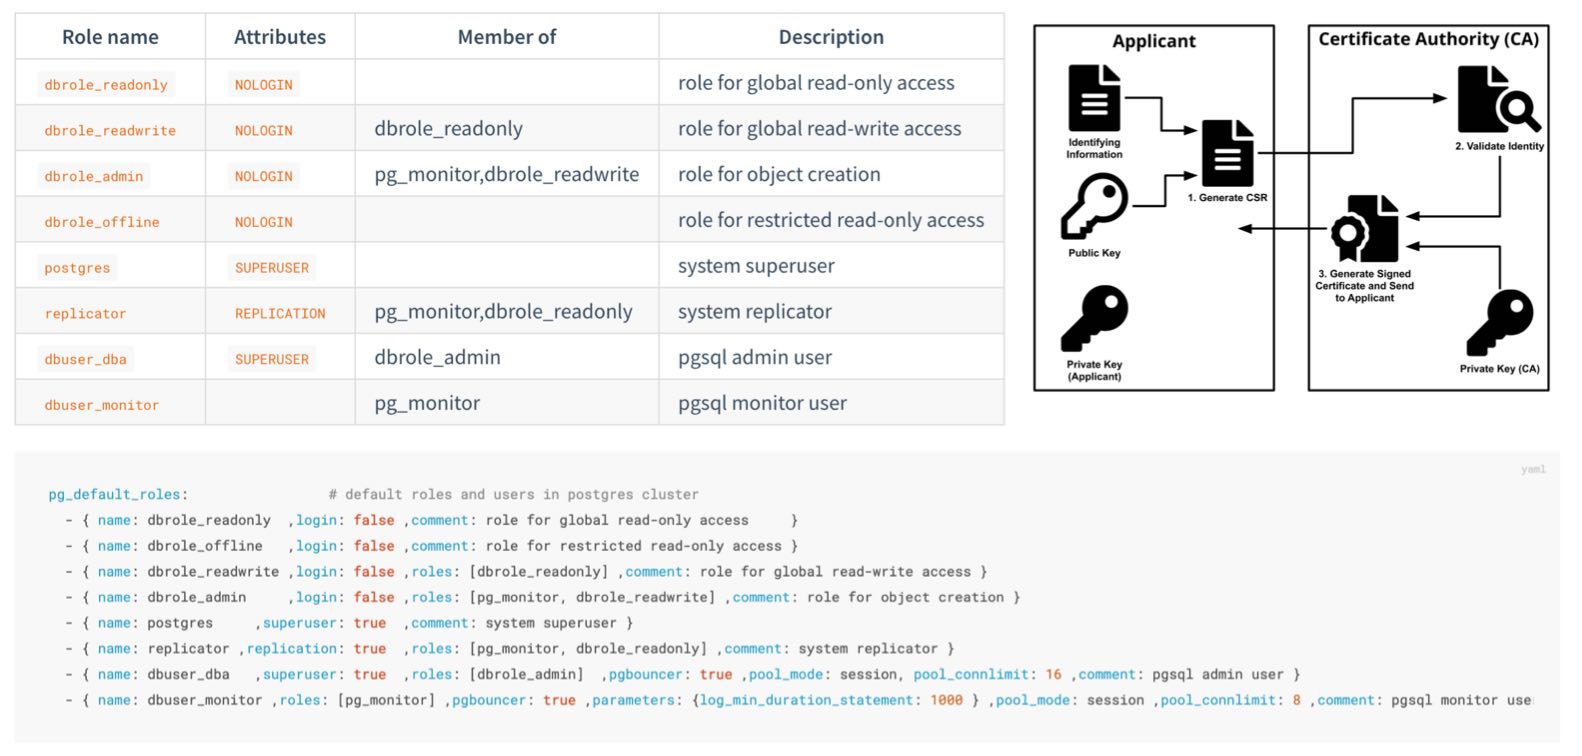
Role System
Pigsty creates four business roles by default. They form privilege groups and cannot log in:
| Role | Attribute | Inherits | Purpose |
|---|---|---|---|
dbrole_readonly | NOLOGIN | — | Global read-only access |
dbrole_readwrite | NOLOGIN | dbrole_readonly | Global DML access; the default choice for application accounts |
dbrole_admin | NOLOGIN | dbrole_readwrite, pg_monitor | Object creation and DDL for administration and release workflows |
dbrole_offline | NOLOGIN | — | Independent read-only role that can be restricted to offline instances through HBA |
Pigsty also creates four system users, each with a specific responsibility:
| User | Attribute | Purpose |
|---|---|---|
postgres | SUPERUSER | Database superuser; no password and local ident login only |
replicator | REPLICATION | Streaming replication and backup, with pg_monitor and read-only privileges |
dbuser_dba | SUPERUSER | Routine administration user that inherits dbrole_admin |
dbuser_monitor | — | Monitoring user with only pg_monitor and read-only privileges |
Application accounts join role groups through the roles field and inherit their privileges:
Customize the declarative role system through pg_default_roles. This parameter replaces the complete list. Retain all required system users and default roles. Also check references in HBA rules, default privileges, and scripts.
Default Privileges
Roles define who receives privileges. Default privileges give newly created objects the required grants automatically.
PostgreSQL provides ALTER DEFAULT PRIVILEGES. Pigsty declares these rules through pg_default_privileges:
The read-only role can query data and execute functions. The read-write role also has DML privileges. The administrator role adds privileges needed for object management.
Ownership Convention
Default privileges apply only to objects created by identities with those defaults configured. Pigsty configures them for:
- the database OS user
pg_dbsu, which defaults topostgres; - the administration user
pg_admin_username, which defaults todbuser_dba; dbrole_admin;- each database owner declared in
pg_databases.
Application DDL should normally run as the declared database owner. Administration and release workflows can use dbuser_dba or first run SET ROLE dbrole_admin. Other users need their own ALTER DEFAULT PRIVILEGES configuration. Otherwise, objects they create do not receive this default privilege model.
PostgreSQL default privileges follow the object creator. They do not propagate automatically from the database or session login name. This is PostgreSQL behavior, not a Pigsty limitation.
Database Isolation
By default, PostgreSQL grants database CONNECT to PUBLIC. If HBA permits it, a login role can enter a database it does not own. Restrict this default when multiple applications share a cluster.
Set revokeconn in a database definition to revoke public connection access:
This revokes CONNECT from PUBLIC. It grants access explicitly to the replication, monitoring, and administration users and the database owner. The owner receives GRANT OPTION and can grant access to others. Without additional grants or inherited roles, app_a cannot connect to app_b.
Cluster initialization also revokes CREATE from PUBLIC on the database and the public schema:
Ordinary users cannot freely create objects in public databases or schemas. This reduces risks from unsafe search_path settings and object shadowing. PostgreSQL 15 restricted the default CREATE privilege on the public schema. Pigsty applies this boundary to all supported major versions.
Offline Role and Instance Isolation
dbrole_offline provides independent read-only privileges for ETL, reporting, and ad hoc queries. It controls object access, not which instance accepts connections.
The default intranet HBA rule for +dbrole_offline has no role filter, so it applies to every instance. To restrict it to pg_role: offline or a replica with pg_offline_query: true, change the complete pg_default_hba_rules list:
pg_default_hba_rules replaces the entire list; do not use the example rule alone. HBA limits expensive queries to offline instances only if it filters by instance role. Users must also lack other inherited roles permitted by broader rules. Add a dedicated service endpoint, connection limits, and query resource controls for resource isolation.
Beyond the Database
Least privilege also applies at the host level:
- The
postgressuperuser has no password and permits only localidentlogin. Its sudo access defaults to required database service and log commands (pg_dbsu_sudo:limit). dbuser_monitorhaspg_monitor, the read-only role, and privileges on themonitorschema. By default, it cannot write business tables.replicatorreceives only directory function privileges needed for backup and recovery, without general superuser access.
Next
- 📖 Complete role and privilege reference: Access Control Configuration
- 🔑 Authentication: the first gate before authorization
- 🔒 Data Security: protection beyond privileges
Was this page helpful?
Thanks—your feedback helps us improve this page.
What got in the way? (optional)