Web Interface
The default single-node installation includes the INFRA module. This module installs an Nginx web server on the node. Nginx supplies the Web UI and proxies requests to the monitoring services and other component interfaces.
Access
Enter the deployment node IP address in your browser.
By default, Nginx uses port 80 for HTTP and port 443 for HTTPS.
Replace 10.10.10.10 in these examples with your node IP address.
| Direct IP Access | Domain (HTTP) | Domain (HTTPS) | Demo |
|---|---|---|---|
http://10.10.10.10 | http://i.pigsty | https://i.pigsty | https://demo.pigsty.io |
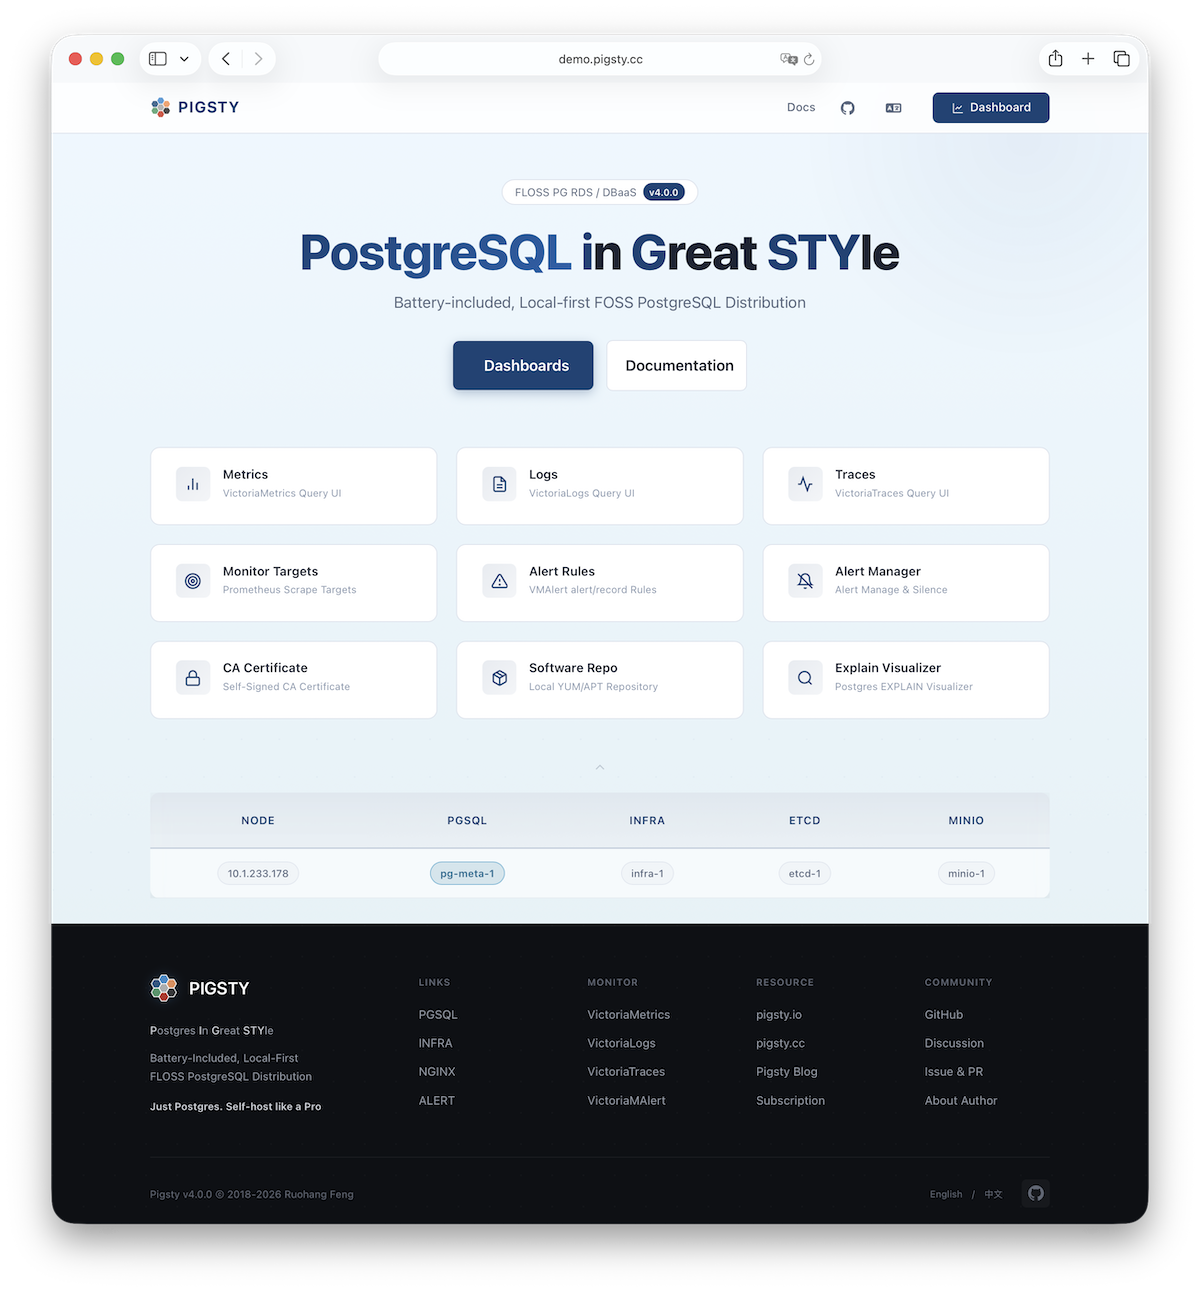
Monitoring
To open the Grafana dashboards, add /ui to the server address:
| Direct IP Access | Domain (HTTP) | Domain (HTTPS) | Demo |
|---|---|---|---|
http://10.10.10.10/ui | http://i.pigsty/ui | https://i.pigsty/ui | https://demo.pigsty.io/ui |
If the service is accessible from the Internet or an office network, use a domain name. Enable HTTPS to encrypt the connection.
Endpoints
Nginx uses these paths to proxy requests to the components. Open each path through the server HTTP or HTTPS address. The native port is the port of the component behind Nginx.
| Endpoint | Component | Native Port | Description | Public Demo |
|---|---|---|---|---|
/ | Nginx | 80/443 | Homepage, local repo, file service | demo.pigsty.io |
/ui/ | Grafana | 3000 | Grafana dashboard portal | demo.pigsty.io/ui/ |
/vmetrics/ | VictoriaMetrics | 8428 | Time series database Web UI | demo.pigsty.io/vmetrics/ |
/vlogs/ | VictoriaLogs | 9428 | Log database Web UI | demo.pigsty.io/vlogs/ |
/vtraces/ | VictoriaTraces | 10428 | Distributed tracing Web UI | demo.pigsty.io/vtraces/ |
/vmalert/ | VMAlert | 8880 | Alert rule management | demo.pigsty.io/vmalert/ |
/alertmgr/ | AlertManager | 9059 | Alert management Web UI | demo.pigsty.io/alertmgr/ |
/blackbox/ | Blackbox | 9115 | Blackbox exporter | |
/haproxy/* | HAProxy | 9101 | Load balancer admin Web UI | |
/pev | PEV2 | 80 | PostgreSQL execution plan visualizer | demo.pigsty.io/pev |
/nginx | Nginx | 80 | Nginx status page (for metrics) |
Domain Access
Point your domain name to the Pigsty server IP address.
Set the domain in the home server configuration.
This configuration is part of infra_portal:
To use a Let’s Encrypt certificate, also set certbot:
After deployment, run make cert to request the free Let’s Encrypt certificate.
If you omit certbot, Pigsty uses the local certificate authority (CA) to issue an HTTPS certificate.
Add the Pigsty CA to your browser trust store before you use that certificate.
You can also configure Nginx to serve local directories or proxy other upstream services. See Nginx Management for the procedure.
Was this page helpful?
Thanks—your feedback helps us improve this page.
What got in the way? (optional)